
INSIGHT DETAIL
What Is Flipper Zero?
Flipper Zero: What It Is, What It Can Do, and What It Cannot Flipper Zero has become one of the most recognizable hardware security tools online.


September 14, 2026
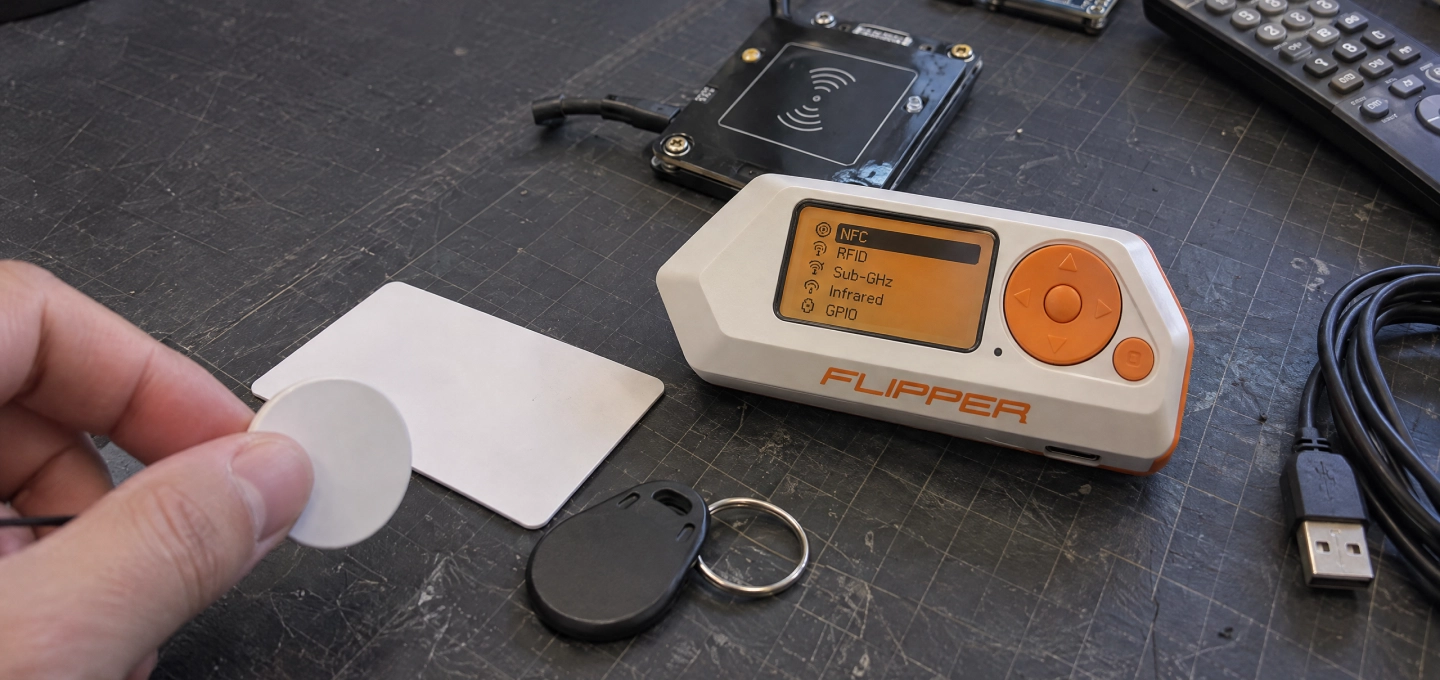
Flipper Zero has become one of the most recognizable hardware security tools online.
Part of that attention comes from short videos showing cards being read, wireless signals being captured, or devices responding to it. Those clips can make Flipper Zero look almost unlimited.
It is not.
What makes the device interesting is that it brings several different technologies into one small tool.
Flipper Zero is a portable device built to interact with technologies such as RFID, NFC, Sub-GHz radio, infrared, iButton, GPIO, and USB.
According to the official Flipper Zero documentation, these functions are built into the device as separate tools for working with different kinds of signals, tags, remotes, and hardware interfaces.
Flipper Zero official documentation
For security researchers, that makes it useful because many everyday systems do not live only inside software.
Access cards, remote controls, wireless sensors, USB devices, and physical access systems all have their own security assumptions.
Flipper Zero can work with supported RFID and NFC tags, inspect certain Sub-GHz signals, interact with infrared devices, and perform authorized USB-based testing.
Its Sub-GHz radio, for example, can receive and work with supported signals used by devices such as gates, barriers, wireless switches, and some remote controls.
But “supported” is the important word.
Flipper Zero cannot automatically copy every access card or control every wireless device.
Some cards can be read or emulated.
Others use stronger authentication or encryption and are much harder to reproduce.
So the answer depends on the technology behind the card, not simply on whether someone owns a Flipper Zero.
That is one reason Flipper Zero RFID and Flipper Zero NFC generate so much interest: the device makes differences between weak and stronger access-control systems easier to see.
Not in the way many viral videos suggest.
Modern vehicle remotes often use changing authentication values or rolling codes rather than sending the same reusable signal every time.
A device interacting with one radio system does not mean it can simply unlock any modern vehicle.
Flipper Zero also includes BadUSB functionality.
In authorized security testing, this can be used to examine what happens when a computer trusts a USB device that behaves like a keyboard.
That makes it relevant to Hardware Security Testing, Endpoint Security, and Penetration Testing.
The device itself is a security and research tool.
What matters is how it is used.
Testing your own hardware or working with explicit authorization is very different from interacting with someone else’s systems without permission.
That distinction is both technical and legal.
Flipper Zero is interesting because it makes one thing very clear:
Cybersecurity is not only about passwords, apps, and servers.
Sometimes the weak point is a card, a radio signal, or a device that trusts more than it should.
Disclaimer
This article is intended for informational, educational, and cybersecurity-awareness purposes only. Flipper Zero and similar security tools should only be used on systems and devices you own or have explicit authorization to test. Unauthorized access or interference may violate applicable laws and regulations.