
INSIGHT DETAIL
Berlin Government Cyberattack
Berlin Government Cyberattack: When State Data Becomes Extortion MaterialA ransomware attack against a government does not always need to shut everything down to create pressure.


September 7, 2026
A ransomware attack against a government does not always need to shut everything down to create pressure.
Sometimes the stolen data is enough.
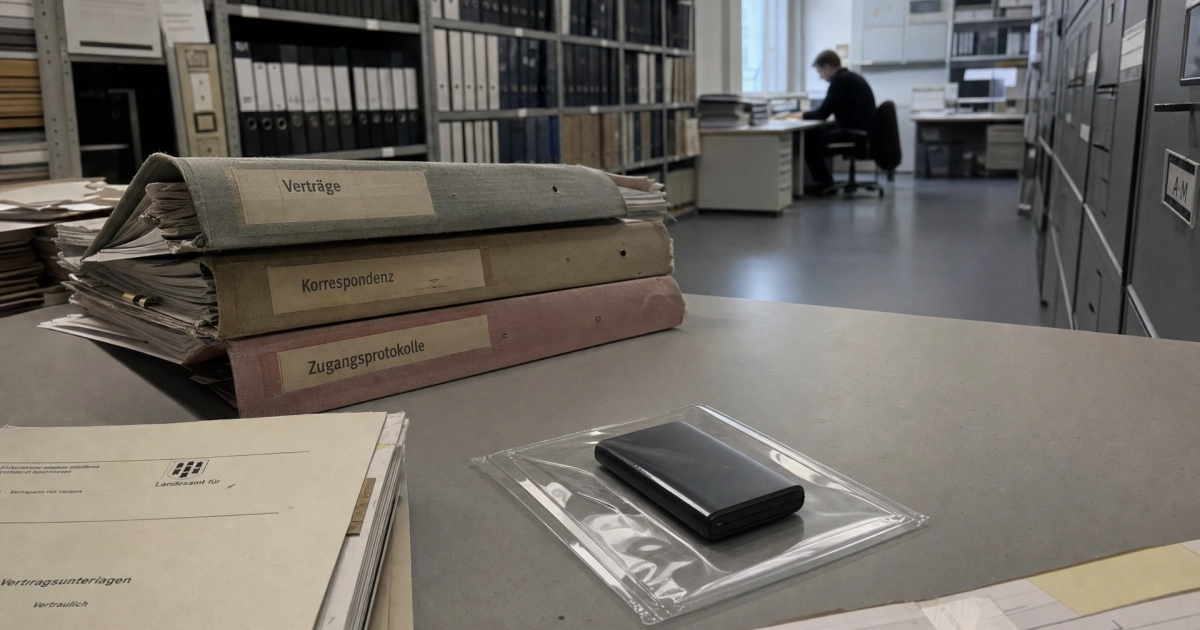
In August 2026, the ransomware group Rhysida claimed responsibility for an attack on Berlin’s state network. The group said it had stolen 5.79 TB of data, including contracts, emails, phone numbers, passwords, and classified information.
This is where Data Exfiltration becomes important.
Data exfiltration means information is copied or removed from a system without authorization.
In a ransomware case, attackers may steal data before they try to encrypt files or disrupt services.
That creates a second layer of pressure.
If the victim refuses to pay, the attackers can threaten to publish or sell the stolen information. This is often called Double Extortion.
For a government institution, that can be especially serious.
The data may include internal documents, personal information, contracts, credentials, or material connected to public-sector operations.
The attack happened less than a month before Berlin’s state election.
Officials said the city’s election infrastructure had not been affected and that no election-related data had been compromised.
That distinction matters.
A cyberattack can happen inside a government network without every system being affected.
Understanding which systems were reached, what data was accessed, and what remained isolated is part of Incident Response.
Ransomware is often discussed as an availability problem: systems stop working, files become encrypted, and services slow down.
But cases like Berlin show the other side.
Sometimes the real value is the information itself.
That is why Access Control, Data Protection, Network Segmentation, and fast incident investigation all matter.
For public institutions, the question is not only whether attackers can enter a network.
It is also what they can take with them.,
Disclaimer
This article is intended for informational and educational purposes only. It does not constitute legal, technical, governmental, or cybersecurity advice. Incident details and findings may change as investigations continue.